What Is Zero Trust and How Does It Strengthen Business Security?
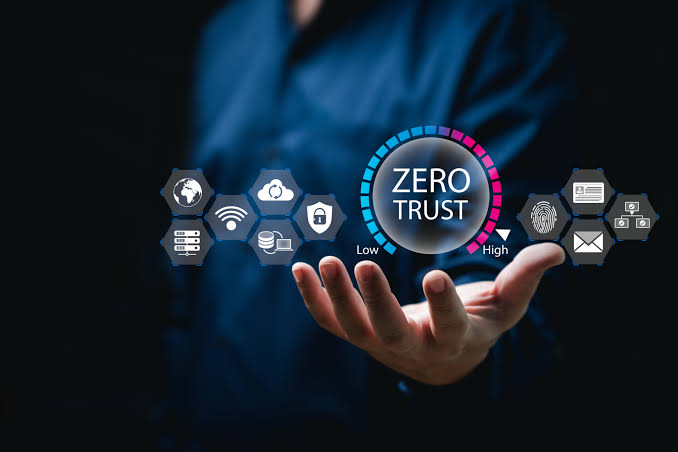
Zero trust is a security model that treats every access request as untrusted until identity, device condition, context, and policy say otherwise. It replaces broad, location-based trust with narrow, continuously evaluated permissions. For businesses managing cloud workloads, remote users, contractors, and aging internal systems, that shift can limit how far an attacker gets after the first compromise.
Now, picture a mid-size financial services firm running its core applications from a hybrid cloud network. Here, employees connect from managed laptops, vendors access selected systems, and service accounts move data between platforms. So, a stolen password shouldn’t open the whole estate, yet in many networks, it still can.
That’s the problem zero trust is meant to address. Not by promising that breaches won’t happen, but by reducing the access, time, and freedom an intruder receives when one does.
What Zero Trust Means in Enterprise Security
Zero trust isn’t a single product or a project that ends after an identity rollout. It’s an operating model built around repeated verification, least-privilege access, and the assumption that a valid login doesn’t automatically mean a safe session.
Therefore, a practical zero trust security approach asks several questions before granting access:
- Who or what is requesting the resource?
- Is the device known, patched, encrypted, and properly configured?
- Does this identity normally request this resource?
- How sensitive is the requested application or data?
- Should access continue if the risk changes during the session?
Here, the access decision isn’t permanent. A user may pass authentication in the morning, then trigger another check after connecting from an unmanaged device or attempting a privileged action.
The US National Security Agency’s Zero Trust Implementation Guidelines describe zero trust as a model that applies granular, least-privilege decisions while treating the network as potentially compromised. The guidance also stresses monitoring for anomalous activity and continually limiting access, rather than trusting an entity after a single checkpoint.
Is zero trust the same as multi-factor authentication?
No, multi-factor authentication is one control within zero trust. A zero-trust model also considers device health, user behavior, location, resource sensitivity, and session risk before granting or continuing access.
How Zero Trust Strengthens Business Security
The security value comes from restricting what users, devices, applications, and workloads can do after they connect.
It Reduces Lateral Movement
Many serious incidents begin with one compromised account or endpoint. In that case, the first intrusion matters, but the larger loss often occurs later, when the attacker discovers internal systems, reaches higher-value credentials, and moves toward sensitive data.
Zero trust breaks up those pathways. Segmentation, workload-level policies, and identity-aware controls can prevent an ordinary user account from reaching administrative interfaces or unrelated databases.
Now, this won’t make lateral movement impossible, but it will be noisier, slower, and more dependent on further compromises. That gives the SOC a better chance of spotting the activity before it becomes a business crisis.
It Narrows the Impact of Stolen Credentials
Multi-factor authentication helps, but it isn’t enough on its own. Session theft, compromised endpoints, consent-based attacks, and weak service accounts can still provide valid-looking access.
Under the zero-trust framework, credentials are only one signal. Here, access may also depend on device health, user behavior, workload identity, location, resource sensitivity, and the requested action.
The UK National Cyber Security Centre recommends authenticating and authorizing connections based on several signals, including user identity, device status, and location. It also makes an often-missed point: service-to-service requests need authentication too.
It Improves Control Across Hybrid Environments
Traditional perimeter models assume there’s a meaningful “inside”, but for many enterprises, there isn’t.
Applications may sit in several clouds, a private data center, SaaS platforms, and a partner environment. Also, users work from offices, homes, airports, and customer sites. Zero trust applies policy around resources and identity instead of relying on network location as proof of legitimacy.
That makes access rules more portable. It also exposes inconsistencies that older network designs tend to hide.
Can zero trust work with legacy systems?
Yes, although legacy systems may not support modern identity and policy controls directly. Organizations can introduce zero trust gradually through segmentation, access gateways, stronger authentication, and tighter monitoring around high-risk legacy applications.
What a Practical Zero Trust Program Requires
So, where should an enterprise begin? Well, certainly not with a company-wide technology purchase, but rather with visibility.
Map Critical Resources and Access Paths
Identify sensitive data, business-critical applications, privileged systems, service identities, and the people who genuinely need access. Also, include legacy applications in that conversation because they are usually where neat architecture diagrams meet awkward reality.
The National Cyber Security Centre places knowledge of users, devices, services, and data at the start of zero trust design. Without that inventory, teams can’t write credible access policies or predict which older systems will resist integration.
Strengthen Identity Without Creating Constant Friction
Use strong authentication for users, administrators, devices, and workloads, then apply additional checks based on risk.
Now, prompting every employee repeatedly here may look strict on paper, but it can produce fatigue and workarounds. Instead, higher-risk actions, such as changing payment details or creating privileged accounts, deserve more scrutiny than opening a low-sensitivity internal page.
Remember, good policy is selective, not merely aggressive.
Apply Least Privilege in Manageable Stages
Trying to redesign every permission at once often stalls the program. So, pick a meaningful use case like third-party access, cloud administration, finance systems, or developer access to production.
For that use case:
- Document current access.
- Remove stale accounts and unnecessary privileges.
- Define contextual access rules.
- Segment the protected resource.
- Monitor denials, exceptions, and unusual behavior.
- Review whether the policy disrupts legitimate work.
Then move to the next area. Small deployments reveal operational problems before they spread across the enterprise.
Connect Policy with Detection and Response
Zero trust shouldn’t operate separately from the SOC. Access decisions, device signals, identity anomalies, segmentation events, and policy denials should feed investigation and response workflows.
For instance, consider a user who authenticates correctly but begins querying repositories they’ve never touched. The right response here may be step-up authentication, session termination, temporary isolation, or analyst review.
It means the context decides the action. Also, without that feedback loop, continuous verification becomes a slogan rather than a control.
How long does zero trust implementation take?
There’s no fixed timeline because zero trust is an ongoing security program, not a one-time deployment. Most organizations begin with a defined use case, such as privileged or third-party access, and expand after testing policies and operational impact.
Common Mistakes That Weaken Zero Trust
The first mistake is treating zero trust as a replacement for every existing security control. It isn’t because endpoint protection, patching, secure configuration, backups, monitoring, and incident response still matter.
The second is focusing only on employees. Machine identities, APIs, workloads, and automation accounts often have broad permissions and weak ownership, which attackers notice.
Another problem is writing policies so strict that teams bypass them. Therefore, security architects need input from application owners, identity teams, network engineers, and the people doing the work. Also, exceptions should be visible, documented, time-limited, and reviewed.
Finally, don’t measure success by the number of tools deployed. Better measures include reduced standing privilege, fewer unmanaged access paths, stronger device coverage, shorter investigation time, and containment of simulated compromise.
Zero Trust Is a Business Risk Decision
Zero trust changes the question from “Is this user inside the network?” to “Should this identity, on this device, perform this action right now?” That’s a more demanding question, but it fits how modern businesses actually operate.
Also, adoption takes time. Legacy technology, inconsistent identity data, ownership disputes, and user friction won’t disappear because the architecture diagram looks sensible. Still, a staged zero trust program can reduce the blast radius of compromised accounts, expose risky access, and give security teams more opportunities to interrupt an attack.
But the strongest programs aren’t built around distrust for its own sake. They’re built around evidence, narrow permissions, and the acceptance that one successful login should never place the wider business at risk.